

Authenticator - Authkey 2FA
by QR Scanner Team
3.5
- Safety
- 100% Safe
- Category
- Tools
- Ratings
- 3.5
- Price
- Free
- Download
- 1.00M
This app is secure, reliable, free to install, and offers fast downloads without any risks or malware.
Screenshots
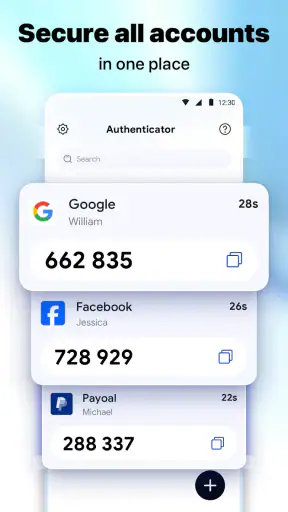
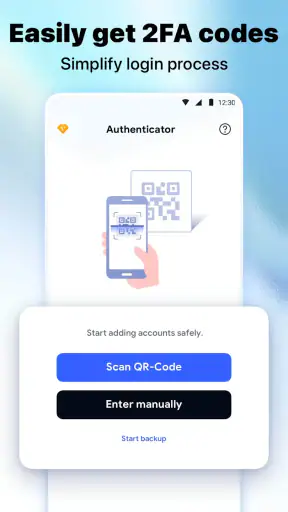
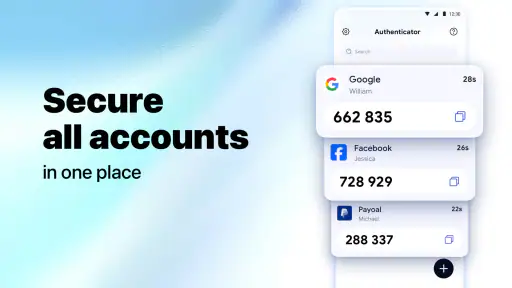
 Analysis by Getfullapps
When an account asks for a six-digit verification code, I want the process to be quick, clear, and dependable. Authenticator - Authkey 2FA is a free tools app from QR Scanner Team that focuses on that single job: generating codes for two-factor authentication. I found it most useful when I treated it as a small daily utility rather than a complete security manager. It does not need to be complicated to earn a place on a phone, but it does need to fit smoothly into the moments when I am signing in.
The app is aimed at people who want a dedicated authenticator instead of relying on text messages or searching through email for a temporary code. Its store short description is simply “Authenticator,” while its broader summary presents it as a way to simplify verification and protect account access. That description is narrow, and in my experience the narrow focus is also the main appeal. I can open it, find the account entry, read the current code, and return to the sign-in screen without dealing with a larger password-management workflow.
It is available at no upfront cost, carries an Everyone age rating, and runs on Android six or later. The current release is version 1.1.5. The app has passed one million installs, with an average rating of 3.5 from roughly 1,700 ratings. Those figures suggest a widely tried utility with a mixed reception rather than a universally polished favorite, so I would approach it as a practical option that deserves a careful setup rather than an automatic recommendation for every user.
How the everyday verification workflow feels
I find the everyday flow easiest to judge by paying attention to the handoff between the account asking for verification and the code on my phone. A calm setup makes that handoff feel routine; a rushed one can turn a simple sign-in into guesswork. I also watch for small habits that prevent avoidable mistakes, especially when several account entries look alike. That practical baseline makes the next choices about setup and upkeep easier to assess.
Starting with an account
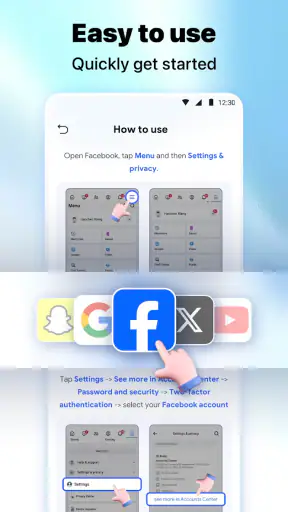
The normal workflow begins when a service offers an authenticator as a second verification method. I open the service’s security settings, choose the authenticator option, and look for the QR code or setup key. In Authenticator - Authkey 2FA, the useful habit is to keep the app open on one device while completing the account setup on another whenever possible. That makes scanning straightforward and avoids the awkward cycle of switching between screens on a single phone.
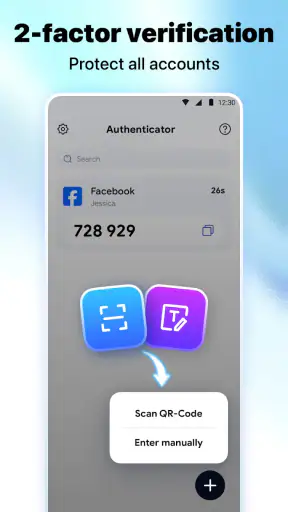
After the account is added, the app’s role is simple: it displays a changing verification code that I enter during sign-in. The most important practical detail is timing. I do not wait until the final second of a code’s cycle before copying it. If the countdown is nearly finished, I wait for the next code and enter that one instead. This small habit prevents avoidable “invalid code” messages caused by submitting a number just as it expires.
For a first setup, I recommend testing the new method immediately while I am still signed in to the account. I sign out only after confirming that the code works and that I have saved the service’s recovery method somewhere safe. This is more important than any visual convenience inside the authenticator. A code generator can help me prove ownership, but it cannot rescue me if I remove the app, lose the phone, and have no recovery route.
Articles to Explore Next

Uber Eats Makes Dinner Easier to Manage, but the Fees Add Up

Google Photos Turns a Camera Roll Into a Library You Can Find Your Way Through

Canva on Mobile: Adopt It for Quick Visuals, Test It for Demanding Work

Google Drive Keeps Work Moving Until It Doesn’t

Switching to Weather - By Xiaomi Means Relearning Your Forecast Routine

Ludo King and the Social Life of a Lucky Six
A realistic daily example
Imagine I am signing in to a work-related account from a laptop at a café. The password is accepted, and the service asks for a verification code. I unlock my phone, open the authenticator, select the relevant entry, and enter the visible code on the laptop. If I am handling several accounts, I check the account label carefully instead of copying the first code I see. That extra second matters because the codes may look similar while belonging to completely different services.
This is where a dedicated tool is more comfortable than receiving a text message. I do not depend on mobile reception, and I am not waiting for a message to arrive. It also keeps the verification step separate from my text inbox, which is useful when I am already sorting through work messages or travel alerts. The trade-off is that I must remember to keep access to the authenticator itself available, especially before changing phones or resetting the device.
What I would prepare before moving accounts
I would not begin by adding every account at once. I would start with one low-risk service, confirm the code process, and then continue with more important accounts. When a service presents a setup key as well as a QR code, I make a private record of that key according to the service’s security guidance. I never leave it in an exposed note or screenshot folder. If the QR code is the only visible setup route, I look for recovery codes before closing the page.
This staged approach makes troubleshooting much easier. If one account fails, I know which setup I just completed. It also prevents a common mistake: assuming that a successful first entry means every later account has been configured correctly. Each account has its own secret and its own recovery process, even though the codes look similar inside the app.
Settings and habits worth checking
For an authenticator, the best settings are often the ones that support clear, safe behavior rather than add more steps. I focus on keeping account names recognizable, the phone’s time accurate, and access to recovery information separate from the device generating codes. Those checks matter most before I depend on the app for an important account or change phones. From there, a few repeatable shortcuts can make regular sign-ins smoother without sacrificing care.
Labels are more important than they seem
Once more than a few accounts are present, clear labels become a security feature in their own right. I use the service name and, when needed, a short identifier such as “personal” or “work.” I avoid vague labels like “login” or “account,” because they force me to guess during a stressful sign-in. A precise label reduces the chance of entering a valid code from the wrong account.
I also check whether duplicate-looking entries are really duplicates before deleting anything. Repeating the setup process for the same service can create two entries with different secrets. Only one may work. Deleting an entry without checking the account’s security page or recovery options can lock me out, so I treat cleanup as a deliberate task rather than casual housekeeping.
Keep the phone ready for the moment of need
The app is most useful when I can reach it quickly. I place it somewhere predictable on my home screen and avoid burying it inside a folder that I rarely open. I also make sure I know how to unlock the phone in situations where a sign-in is likely, such as arriving at an airport, changing a password on a laptop, or setting up a new browser.
That does not mean I disable the phone’s security protections for convenience. The verification codes protect accounts, but the phone also protects the codes. A screen lock, sensible notification behavior, and cautious handling of screenshots are part of the same routine. I do not treat a code as harmless just because it expires; someone who sees it at the right moment may still use it.
Be realistic about paid prompts
The app is free to download, but it includes in-app purchases ranging from $4.99 to $49.99 per item. That is worth noticing before I recommend it to someone who expects every part of a basic authenticator to remain free. I would inspect any purchase screen carefully and decide whether the free experience already covers my needs before paying for anything.
For my own use, the deciding question is not whether a paid option exists, but whether it changes a problem I actually have. If I only need codes for a few accounts, a purchase may not be necessary. If a particular extra is important to my workflow, I would first compare its value with another authenticator that offers the same core function under a different pricing model. The presence of purchases does not make the app unsuitable, but it does make the cost structure part of the decision.
Use repeatable checks after an update or phone change
The current version is 1.1.5, and I would still use the same cautious habit after any update: open the app before I need it, confirm that my entries are visible, and test an account only when I can safely recover from a problem. I do not assume that changing phones will automatically carry every authenticator entry across. Before replacing a device, I review each service’s transfer, export, or recovery instructions rather than relying on memory.
This is one of the less obvious differences between an authenticator and a normal notes app. The entries are not merely information I can casually recreate later. They are part of a cryptographic sign-in arrangement. A tidy list today is not enough; I need a repeatable migration habit for tomorrow.
Faster patterns for experienced users
When I use an authenticator often, speed comes from preparing the surrounding routine, not from rushing through the code itself. I keep the sign-in page ready, know which account entry I need, and wait for a fresh code if the current one is close to expiring. I also reserve account setup and list cleanup for a quiet moment, so an urgent login does not become the time I discover a mistake. These habits help reveal where convenience ends and the app’s limits begin.
Separate setup time from sign-in time
I get better results when I do not configure accounts in the middle of an urgent login. Setup belongs in a calm session, with recovery codes available and another device nearby if possible. Sign-in should then be a short routine: open the authenticator, identify the account, use a fresh code, and close the app.
This separation also helps me notice mistakes earlier. If I configure an account while rushing, I may skip the test login, mislabel the entry, or forget where the recovery information went. A separate setup session turns authentication into a checklist instead of a last-minute puzzle.
Use the code cycle instead of fighting it
A common beginner reaction is to rush when a code is close to expiring. I do the opposite. I glance at the remaining time, wait for a fresh cycle when necessary, and then type deliberately. On a laptop, I keep the sign-in page ready before opening the app. On a phone, I avoid switching repeatedly between the browser and authenticator if that makes me lose my place.
When a code fails, I do not immediately delete the entry and start over. I first check the account label, the device’s automatic date and time, and whether I accidentally used an older code. Time synchronization is a particularly important troubleshooting step because authenticator codes depend on both the secret and the current time. A wrong clock can make a correctly displayed code fail.
Build a recovery routine, not just a code routine
The strongest workflow combines the app with the recovery tools offered by each service. I store recovery codes in a secure place separate from the phone, and I know which account recovery method I would use if the device disappeared. I also avoid keeping the only copy of a setup secret inside the same phone that generates the code.
This may sound excessive for a simple tools app, but it is the difference between convenient two-factor authentication and a lockout risk. Authenticator - Authkey 2FA can generate the temporary code; it does not replace the broader account-recovery plan. Anyone who travels, changes phones often, or manages work accounts should treat that plan as essential.
Choose the right moment to clean the list
I remove an entry only after disabling authenticator verification on the corresponding service or confirming that the service has another working method. I do not clean up by appearance alone. An old-looking entry may still be the active key, while a newly created entry may be the one that works.
A useful maintenance session is to review the list alongside the security pages of the accounts. I check names, remove services I no longer use, and confirm that recovery options are current. This keeps the app readable without turning deletion into guesswork.
Where the app reaches its limits
I judge the app’s limits by asking what happens when the phone is unavailable, an entry is confusing, or I need more than code generation. Those are not edge cases for people who travel, manage work accounts, or replace devices; they are part of choosing an authentication method responsibly. A dedicated code app can suit a straightforward routine, while a password manager or hardware security key may fit other needs better. That distinction frames my overall verdict.
It is not a full password manager
I would choose this app for code generation, not for organizing passwords, secure notes, passkeys, or a wider identity-management system. If I want one protected vault that fills passwords and handles multiple authentication methods, a dedicated password manager may be a better fit. Combining tools can be less convenient, but it may also give me a clearer separation between passwords and verification codes.
Likewise, people who expect a seamless multi-device experience should examine the app’s behavior during their own setup before moving every account. The practical question is whether the workflow they need—transfer, backup, or access from another device—is available and comfortable for them. I would not build a critical account strategy around an assumption that has not been tested.
It depends on disciplined device management
The app is only as dependable as the phone carrying it. A dead battery, lost device, forgotten screen lock, or careless reset can interrupt access. This is not a flaw unique to Authkey 2FA, but it is a real limitation of phone-based authentication. Text-message codes may be easier to recover in some situations, while a hardware security key may offer stronger protection against certain attacks.
For sensitive accounts, I prefer to consider more than one authentication method when the service supports it. An authenticator is usually more secure than relying only on text messages, but it is not automatically the best answer for every threat model. A security key can be a better choice for someone protecting high-value accounts and willing to carry extra hardware. A password manager may be better for someone who values synchronized access and consolidated account maintenance.
The rating reflects a product that needs personal testing
With a 3.5 average and about 1,700 ratings, I would not describe the app as an unquestioned leader. That does not make it unusable. It tells me to test the exact workflow I care about before moving important accounts. I would add one account, verify the code, inspect the available controls, and only then decide whether the experience is stable enough for broader use.
The app has also accumulated more than one million installs and 48 reviews, so it is not an obscure experiment with no user base. Still, popularity alone cannot answer whether its organization, recovery process, and purchase prompts suit me. Authenticator tools are personal utilities: a small difference in handling can matter more than a large install count.
My verdict after making it part of a routine
Authenticator - Authkey 2FA works best for someone who wants a focused code generator and is willing to manage setup carefully. I like the straightforward purpose, the offline-style convenience of having codes available on the phone, and the way it keeps verification separate from text messages. For everyday sign-ins, the workflow is easy to understand once the accounts are labeled and tested.
I would recommend it to a casual or moderately experienced user who needs an authenticator for several services and prefers a dedicated tools app. I would also recommend starting slowly: configure one account, test it, save recovery information, and then expand. That approach gives the app a fair evaluation while protecting the accounts that matter most.
I would skip it if I need a complete password vault, a clearly established multi-device system, or a security-key-centered setup. I would also hesitate to make it my only access route for critical accounts before confirming how I will recover everything after a lost or replaced phone. In those situations, another authenticator, a password manager, or hardware-based security may better match the job.
My final view is positive but measured. This is a useful free starting point, not a substitute for an account-security plan. The people who get the most from it are the ones who combine the app with accurate labels, automatic time settings, fresh-code timing, recovery codes, and a deliberate phone-change routine. The real strength is not simply displaying a code; it is making that code part of a repeatable sign-in habit. For that focused purpose, Authenticator - Authkey 2FA is worth trying, provided I keep its limits and its optional purchase model in mind.
Pros
- Supports multiple accounts in one app
- Works offline for generating verification codes
- Simple setup with QR code scanning
- Compatible with most services using TOTP 2FA
- Helps protect accounts beyond password-only security
Cons
- Losing the device may complicate account recovery
- Backup and transfer options may require extra attention
- Some advanced security features may be limited
- QR scanning depends on camera permissions
- Not all services support the same authentication method
FAQs for Authenticator - Authkey 2FA
What is Authenticator - Authkey 2FA used for?
Authenticator - Authkey 2FA is designed to add an extra layer of security to online accounts through two-factor authentication. After you link a supported service, the app generates temporary verification codes that you enter after your password. This means that even if someone discovers your password, they still need the current code from your authenticator to complete the sign-in.
How do I add an account to Authenticator - Authkey 2FA?
Most services let you connect the app by scanning a QR code displayed in their security settings. Open Authenticator - Authkey 2FA, choose the option to add an account, and scan the code. If scanning is unavailable, you can usually enter the setup key manually. Always confirm that the six-digit code matches the service before finishing the setup.
Does Authenticator - Authkey 2FA work without an internet connection?
In general, time-based authentication codes can be generated without mobile data or Wi-Fi once an account has been configured. The codes are based on a shared secret and the device’s clock rather than a live internet connection. However, accurate time settings are important. If codes are rejected, check that your phone is using automatic date and time before trying again.
What happens if I lose my phone or delete the app?
Losing access to your phone can make account recovery difficult if your authentication entries are stored only on that device. Before relying on Authenticator - Authkey 2FA, save each service’s backup or recovery codes in a secure location and check whether the app offers an encrypted backup or transfer feature. Recovery options ultimately depend on the individual website or service.
Is Authenticator - Authkey 2FA safe to use?
An authenticator app is generally safer than receiving verification codes by SMS because it reduces exposure to phone-number attacks and message interception. Nevertheless, security also depends on how you protect your phone and account. Use a screen lock, install the app from an official store, avoid sharing setup keys, and review the app’s permissions and backup options before adding important accounts.

Authenticator - Authkey 2FA
This site provides independent information about third-party apps and is not affiliated with, or the owner, developer, or distributor of, any app featured here. App names, logos, and trademarks belong to their respective owners. Developer details are provided for reference; please contact the developer directly via authdev_sup@outlook.com, visit https://adqr.qrscanner.cc/authenticator-app/, or review their https://adqr.qrscanner.cc/authenticator-app/privacypolicy.html.










